SAST analysis
Static rules plus AI
The rules detect known patterns in a reproducible way. The AI explains the context, prioritizes and proposes the fix. The result is a clear finding, not a list of scattered alerts.
Upload your code and get a report with explained findings, the affected snippet, the proposed fix and the estimated effort to apply it. Static rules and AI models work together, with the structure of a professional report.
The free account gives access to the demo reports.
For cybersecurity consultants, expert developers, development teams and those responsible for regulations and standards.
The rules detect known patterns in a reproducible way. The AI explains the context, prioritizes and proposes the fix. The result is a clear finding, not a list of scattered alerts.
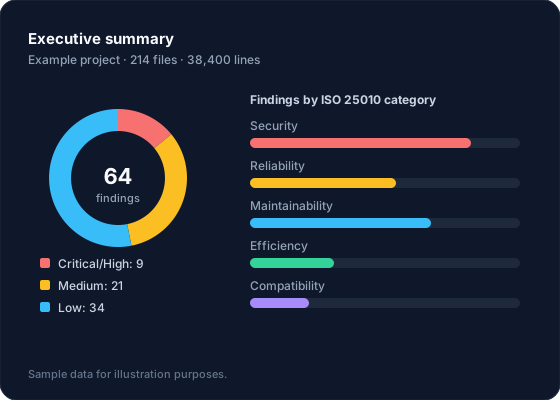
Charts and indicators to decide, and the detail of each finding to fix it. Download as HTML (printable to PDF) or Markdown, organized by date and by project.
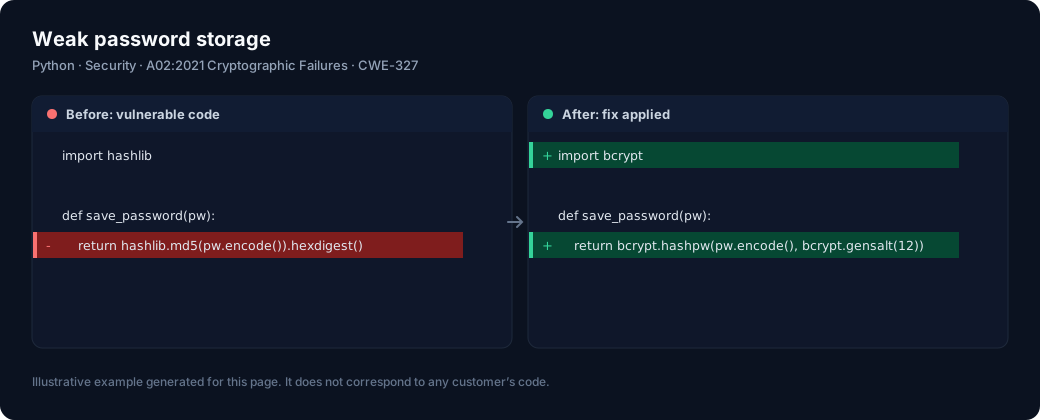
Each finding shows the affected code, the fixed code with the differences highlighted and the estimated time to apply the change, including execution tests.
From file to report in four steps, with a clear cost before you start.
A compressed file with the source code as text, or connect your GitHub account in read-only mode.
We verify the content, compute its digital fingerprint (hash) and show you the files, lines, effort and approximate credits.
You confirm your authorization over the code and the estimated credits. The analysis runs in the background.
You will find it in the Reports section, ready to view, print to PDF or download as Markdown.
Three illustrative examples of the kind of finding and fix you will see in a report.
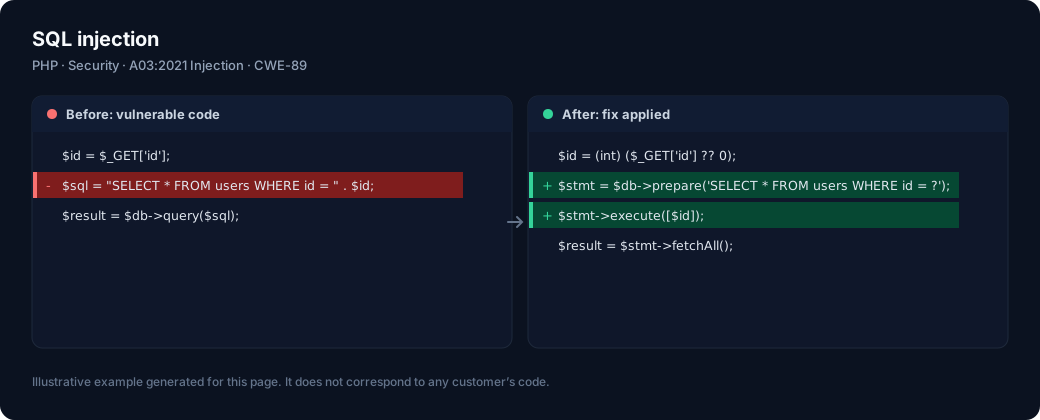
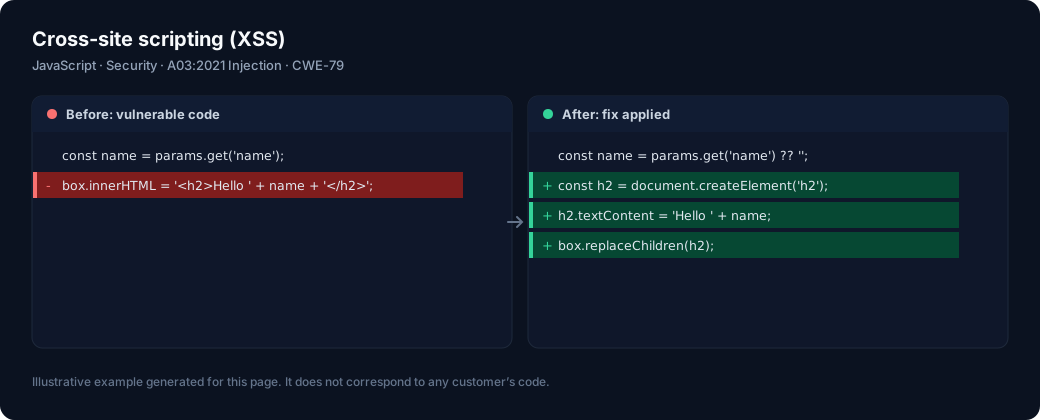
Each finding is classified into one of the ISO/IEC 25010 quality characteristics and highlighted with its own color. For Security we focus on the OWASP Top 10, with CWE references where they apply.
“Aligned with” means that we use these frameworks as the basis for classification. It does not imply certification or accreditation.
The users of this platform are security professionals, and the service was designed to meet that standard.
You create your account for free and buy the credits you need. Each analysis uses credits according to the size and complexity of the code. Analyze your code as many times as you want.
With your free account you can view and download three example reports with fictitious information, without buying credits.
If you need a tailored solution, a deeper analysis of your company’s code or an answer to a question before you start, write to us and we will reply.